Manage users
For user management, go to Management > Users

You can invite new users by clicking the "Invite new user" button on the top of the page.
Roles
Associated permissions are described below:
| Permissions/Roles | Admin | Editor | Viewer |
|---|---|---|---|
| View Model and Custom Rules configuration | ✅ | ✅ | ✅ |
| Edit Model Responses and Custom Rules | ✅ | ✅ | - |
| Enable/Disable Model and Custom Rules | ✅ | - | - |
| Delete a Custom Rule | ✅ | - | - |
| Access to the Management section | ✅ | ✅ | - |
| View Users | ✅ | ✅ | - |
| Manage Users | ✅ | - | - |
| Edit Trusted Proxies | ✅ | - | - |
| Enable/Disable Global Protection | ✅ | - | - |
Multi-Factor Authentication (MFA)
The MFA column shows whether each user has MFA set up:
- Green check: MFA enabled.
- Red cross: MFA disabled.
- Empty: the user has never logged in to this organization, so their status isn't shown.
Admins see the status of every user. Other users only see their own.
When enabling MFA for all usersAs an admin user, if you have enforced the MFA feature for all your users, the status will be enabled as soon as the users finish the activation on their end.
Reports & Notifications

Email Reports
Email reports are useful to get statistical insights about threats and your relevant protection status.
You can manage which users will receive the email reports on a daily or weekly basis, or both.
Email notifications
Email notifications are useful to be warned about attacks blocked by DataDome.
As soon as an attack is being blocked on any of your endpoints, you will receive an email with all the relevant information about it.
You can manage which users will receive this information.
You also can choose which types of attacks you want to be warned about, or select all of them.
Actions
MFA Activation (Admin users only)Please note that you won't be able to activate the Multi-Factor Authentication for a user on this page. As an admin user, when you'll activate the Multi-Factor Authentication on the Account Security page, every user will have to enroll MFA during their next login.
Please contact our support team to reset MFA on an admin account
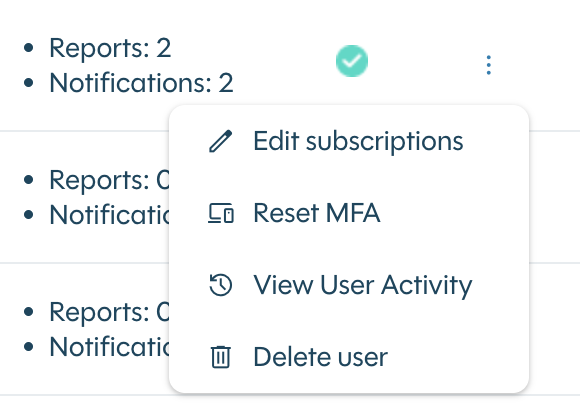
From the actions menu on a user's row, you can:
- Edit subscriptions: choose which email reports and notifications the user receives.
- Reset MFA: disable MFA for the user by removing all of their enrolled factors. This can't be undone. If your organization enforces MFA, the user must set up a new factor at their next login. Otherwise, they log in with their password only until they add a factor again from their Profile page.
- View User Activity: open the audit trail filtered on this user, if your plan includes it.
- Delete user: remove the user from the organization. Users managed by SCIM must be removed in your identity provider.
Updated 6 days ago